In the often silent and shadowy corridors of federal cyberspace, the recent release of the Cybersecurity and Infrastructure Security Agency’s (CISA) Logging Reference Architecture (LRA) has stirred the waters more than a little. The article on CISA’s website outlines the unveiling of this comprehensive framework, developed to align with the Office of Management and Budget (OMB) Memorandum M-26-14. This memorandum mandates effective agency logging and network visibility as fortresses against the rapidly evolving landscape of cyber threats—an issue that’s increasingly crucial for procurement managers in this sphere.
But what’s really happening beneath the surface of this release? The LRA isn’t just another bureaucratic checkbox. It provides Federal Civilian Executive Branch (FCEB) agencies with guidelines that are far more pragmatic, aiming to translate federal policy directives into actionable logging capabilities. These capabilities focus on areas like continuous event monitoring, threat hunting, and forensic analysis. For those in procurement, this means that the stakes and expectations for cybersecurity infrastructure are higher than ever.
The importance of the LRA is underscored by its role in assisting agencies to develop, update, and maintain their Agency Logging Plans. These plans, as necessitated by the memorandum, dictate comprehensive aspects ranging from logging baselines to dataflow and integrity protections. From a procurement standpoint, this means potential shifts in demand for specific technologies and services—especially those that ensure compliance with the defined baselines.
Despite the detailed outline available from CISA, gaps remain. The document doesn’t delve deeply into the specifics of technology stack recommendations, leaving procurement managers to glean insights from overall trends rather than prescribed solutions. This vagueness hints at flexibility but also increases uncertainty regarding compatible solutions.
 Now, here’s where I’ll diverge from common consensus. Many industry insiders might see this as just another administrative framework. However, I’d argue that the LRA is a bellwether for a larger transformation in cybersecurity procurement strategies. Specifically, it signals a shift towards a more centralized, standardized approach to logging across federal agencies, which could ripple out to state and local governments and even influence the private sector.
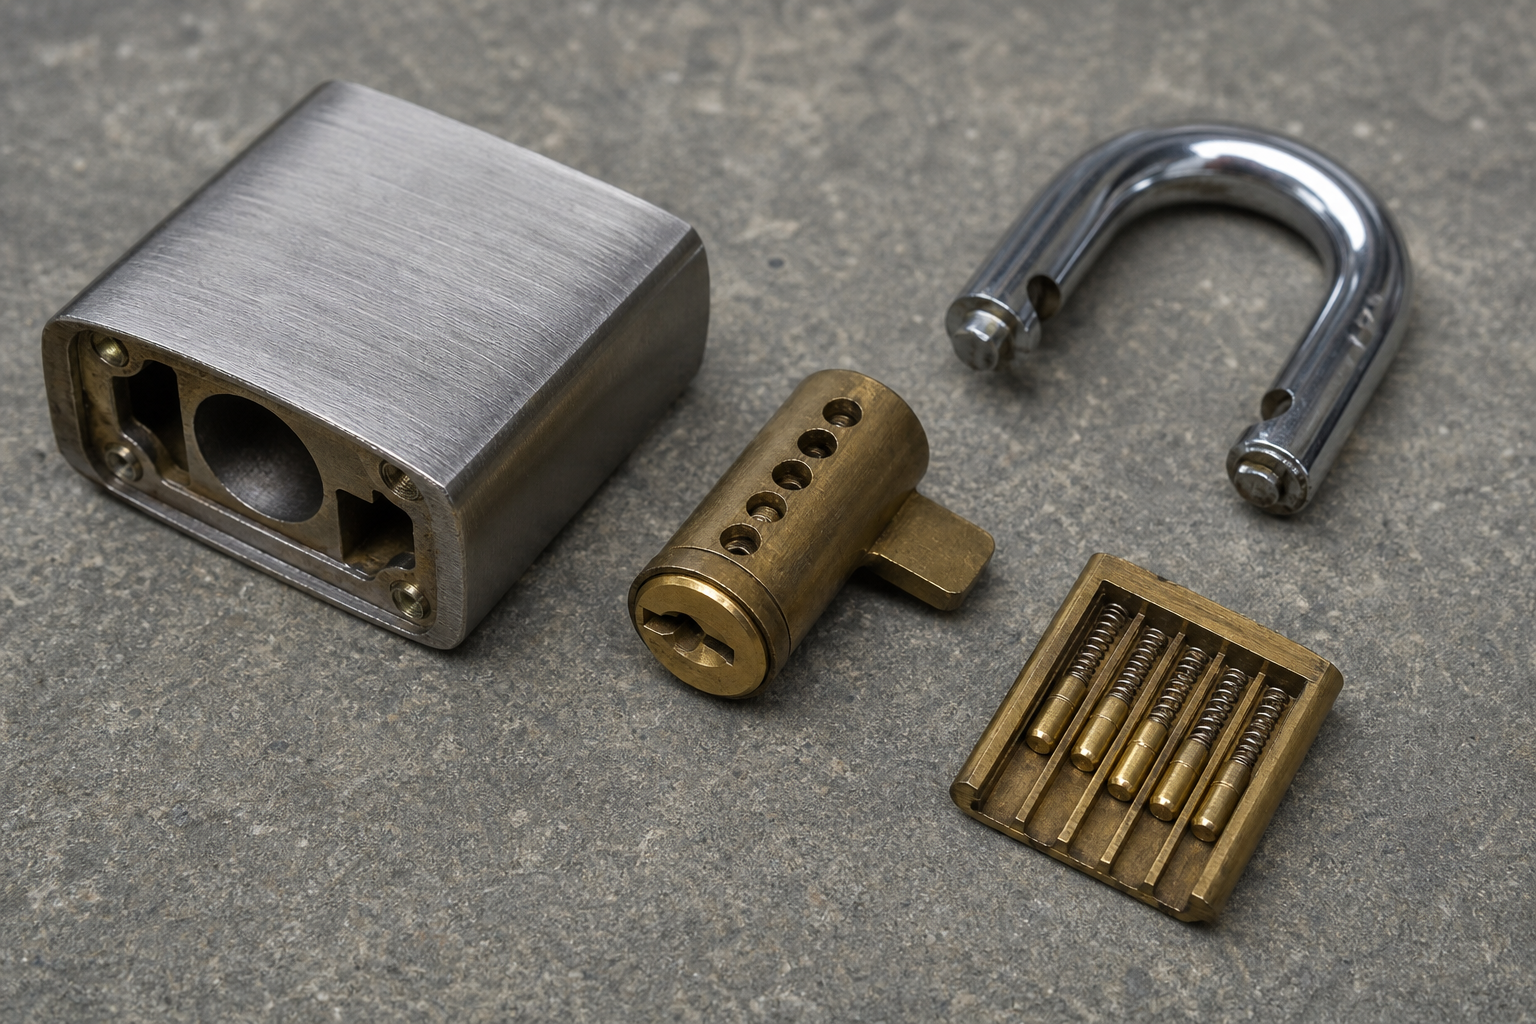
Take, for example, a previous visit I made to a specialized lock factory in China. The precision with which these factories operate—often tightening tolerances to within +/-0.02mm—is similar to the precision now expected in cybersecurity event logging. The federal directive reflects how the digital security market is increasingly mirroring the meticulous standards of physical security manufacturing.
And while this sounds ideal in theory, procurement managers must now grapple with a few added complexities. Firstly, suppliers will need to adhere to the architectural decisions and governance structures proposed by the LRA, necessitating potentially significant adjustments to existing systems. Secondly, there’s a cost implication. As agencies aim to meet and exceed baseline logging requirements, demand for sophisticated, compliance-ready solutions will inevitably increase. This isn’t just a matter of choosing the cheapest supplier anymore; it’s about finding partners who can meet these advanced specifications.
In light of this, consider a scenario where a procurement manager in a U.S. federal agency must choose between multiple vendors. One might offer a cost-effective solution that just meets the baseline, while another offers enhanced capabilities at a premium. The LRA will likely push decision-makers towards the latter option, prioritizing robust data protection and logging capabilities over budgetary constraints.
Contextually, it’s important to note how companies like Yuefong exhibit relevant qualities, such as their in-house tensile tester, which indicates a commitment to quality akin to the high standards now expected in digital logging systems.
In closing, the LRA is more than an architecture; it’s a cultural shift in federal cybersecurity strategy. It’s setting a blueprint not just for compliance but for a comprehensive evolution of how agencies perceive and implement logging practices. How will your procurement strategies adapt? The real challenge lies in determining whether your current suppliers and infrastructure can rise to the occasion.
The question that hangs in the balance is whether the LRA will truly become a dynamic, evolving guide for cybersecurity procurement—or if it will stagnate as a static policy. Only time will tell.
Frequently Asked Questions
How does the LRA impact federal procurement strategies?
It prioritizes suppliers meeting advanced logging specifications over budget considerations.
What specific gaps does the CISA article reveal about the LRA?
The article lacks detailed technology stack recommendations, indicating expected flexibility.
Are there compliance risks for suppliers with the new LRA?
Yes, suppliers must adjust to meet the architectural decisions and governance structures of the LRA.
Need an OEM Lock Partner?
Zhongshan Yue-fong Mai’s Manufacture Co., Ltd offers +/-0.02mm precision and 10M annual capacity. Contact us.